Suramya's Blog : Welcome to my crazy life…

June 20, 2023

It is now possible to track someone using SMS Receipt Messages

Filed under: Computer Security,Interesting Sites,My Thoughts,Tech Related — Suramya @ 6:04 PM

With modern technology it is getting more and more easy to track someone. There are many apps, devices etc that allow a target to be tracked in near realtime by someone. This can be done using an App on your phone, find my phone functionality, family phone track etc etc. As someone who is worried about getting tracked they can disable GPS, get a new dumb phone that doesn’t support GPS etc which can mitigate the threat to a large extent. Unfortunately, now there is a new attack surface that allows an attacker to approximately locate a target with up to 96% accuracy.

Researchers have figured out how to deduce the location of an SMS recipient by analyzing timing measurements from typical receiver location. Basically they measure the time elapsed between sending a SMS and the receipt of the Delivery report and then use a ML model to predict the location area where the target could be located. The other advantage of this attack is that it doesn’t require any specialized equipment or access to restricted systems but can be executed via a simple smartphone.

Short Message Service (SMS) remains one of the most popular communication channels since its introduction in 2G cellular networks. In this paper, we demonstrate that merely receiving silent SMS messages regularly opens a stealthy side-channel that allows other regular network users to infer the whereabouts of the SMS recipient. The core idea is that receiving an SMS inevitably generates Delivery Reports whose reception bestows a timing attack vector at the sender. We conducted experiments across various countries, operators, and devices to show that an attacker can deduce the location of an SMS recipient by analyzing timing measurements from typical receiver locations. Our results show that, after training an ML model, the SMS sender can accurately determine multiple locations of the recipient. For example, our model achieves up to 96% accuracy for locations across different countries, and 86% for two locations within Belgium. Due to the way cellular networks are designed, it is difficult to prevent Delivery Reports from being returned to the originator making it challenging to thwart this covert attack without making fundamental changes to the network architecture.

The biggest problem with this method is that it doesn’t depend on any software or anything that needs to be installed on the target phone. You just need a phone that supports SMS, which is pretty much all phones in the market. There is an option to disable delivery reports which would mitigate the threat to an extent but is an opt-out setup rather than an opt-in. One way to reduce this vector would be for manufacturers to disable the delivery report by default and folks who need it can enable it from settings instead of the other way round which is the case right now.

Source: HackerNews: Freaky Leaky SMS: Extracting user locations by analyzing SMS timings
Full Paper: Freaky Leaky SMS: Extracting User Locations by Analyzing SMS Timings

– Suramya
June 12, 2023

A DIY Robot for automating a Cold boot attack now exists

Filed under: Computer Hardware,Computer Security,My Thoughts,Tech Related — Suramya @ 11:58 PM

A Cold boot Attack has been around for a while (It was first demo’d in 2008) but it has been a fairly manual tricky operation till now. But now there is a new DIY Robot has been created that reduces the manual effort for this attack. Now you might be asking what on earth is a Cold Boot Attack? No, it is not referring to having to wear cold shoes in winter. It is actually a very interesting attack where the attacker freezes the RAM chips of a system while it is running and then shuts it down, after which they remove the RAM chip and put it in another device to read the data from it. Because the chip has been cooled significantly it retains the information even after the system is shutdown long enough for information to be extracted from it. The original cold boot attack involved freezing a laptop’s memory by inverting a can of compressed air to chill the computer’s DRAM to around -50°C so that it persists for several minutes, even after the system was powered down.

Ang Cui, founder and CEO of Red Balloon Security has created a process & robot to extract the chip from the system. The robot is a CNC machine which is has a FGPA (field-programmable gate array) connected to it. The robot chills the RAM chips one at a time, extracts them from the board and then inserts them into the FGPA that reads the contents of the chip allowing them to extract the data from it. To make it easier and allow them more time to remove the chip, the system monitors the electromagnetic emanation of the device which allows them to identify when the system is running CPU bound operations. Once they identify that, they can extract the chip when the system is using the CPU and not reading/writing to the RAM. This gives the robot a window of ~10 milliseconds to extract the chips instead of having to do it in nanoseconds.

Cui and colleagues demonstrated their robot on a Siemens SIMATIC S7-1500 PLC, from which they were able to recover the contents of encrypted firmware binaries. They also conducted a similarly successful attack on DDR3 DRAM in a CISCO IP Phone 8800 series to access the runtime ARM TrustZone memory.

They believe their technique is applicable to more sophisticated DDR4 and DDR5 if a more expensive (like, about $10,000) FPGA-based memory readout platform is used – a cost they expect will decline in time.

Cold boot attacks can be countered with physical memory encryption, Cui said.

This is not an attack the average user has to worry about but it is something that folks working on critical systems like banking servers, government systems, weapons etc need to be aware of and guard against. More details on the attack will be provided during a talk at the REcon reverse engineering conference in Canada titled “Ice Ice Baby: Coppin’ RAM With DIY Cryo-Mechanical Robot

Source: Hacker News: Robot can rip the data out of RAM chips

– Suramya

June 10, 2023

The World Book encyclopedia is still in print and I really wanted a copy

Filed under: My Thoughts — Suramya @ 11:59 PM

Back in the early 1990’s we made a big investment and bought a copy of the World Book Encyclopedia. From what I can remember it costed quite a bit but it was worth it. Most of my research for any paper or project I had to do in my school years was done using these as the starting point. (and the middle and the end for most of the research).We still have the encyclopedias at home in Delhi but they are not much used. I think Vir has used them a few times to find something but with the internet putting the latest research at your fingertips the physical books are not that used.

However, there are multiple advantages to having a physical copy of something. For example, we are not dependent on internet connectivity or even electricity to be able to look up something in a physical book. Plus there is just a different feel to having a physical book in your hand rather than a digital copy.

Found a post earlier this week where this journalist found out that the World Book Encyclopedia is still being actively published in physical form every year and I was actually tempted to go and buy the latest version just so that I have it at home. Then I saw the cost for full set and decided that nostalgia is all well and good but not worth spending $1,199. You can also subscribe to an online version of the encyclopedia for lot cheaper cost but I don’t think I am going to do that. I have access to enough other sources where this is not needed.

This reminded me that I do have a CD version of the Encarta Encyclopedia lying around somewhere, maybe I should install it and see if it still works on my new system…

Source: Arstechnica: I just bought the only physical encyclopedia still in print, and I regret nothing

– Suramya

June 5, 2023

Map Directions can’t always be trusted

Filed under: Humor,My Thoughts — Suramya @ 5:49 PM

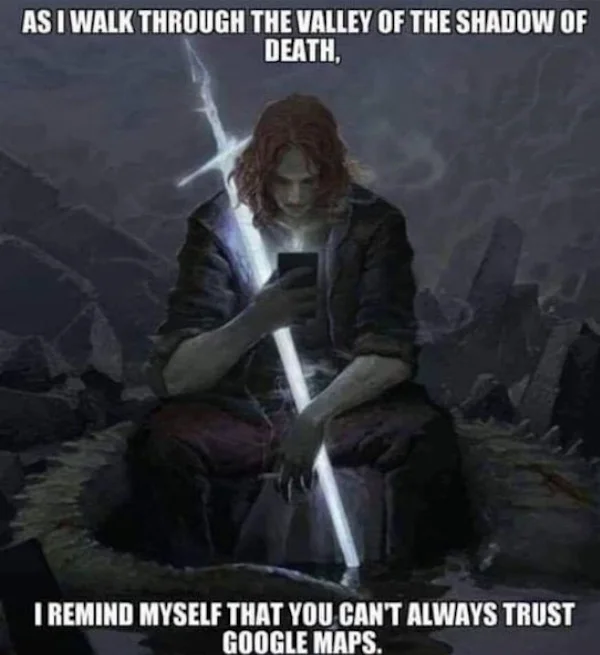
There are too many cases where someone followed Google Maps or Apple Maps blindly and ended up somewhere they weren’t supposed to. Before Google maps was available Map My India was the most up to date option available for maps in India. I remember one time me and Gaurang were on my way to visit friends and the map kept insisting that we take a left from the top of the flyover. This was before the time when algorithms would auto update the route if you missed the turn so it kept insisting that we take a U-Turn and turn from the top of the bridge. Ended up having to restart the session before it gave us an alternative route.


As I walk through the valley of the shadow of death, I remind myself that you can't always trust google maps.
As I walk through the valley of the shadow of death, I remind myself that you can’t always trust google maps.

Even with Google Maps you have to watch where it is trying to take you, I once was directed to take a road that was about six inches wider than my car, (It started a bit wider and narrowed as I drove into it) had to reverse back out of the way before I got stuck there. Apple maps is even ‘better’ in that Australian Police had to release an advisory back in 2012 warning people about its Potentially Life Threatening” Misdirection.

There is no system that is 100% up to date and accurate but it is expected that when you are you following directions, you use your own brain as well once in a while so you don’t end up in the middle of a desert, or drive into a lake or take a longer way to get where you are going.

– Suramya

May 29, 2023

There are Two kinds of people in the world…

Filed under: Humor,My Thoughts — Suramya @ 7:23 PM

There are Two kinds of people in the world…

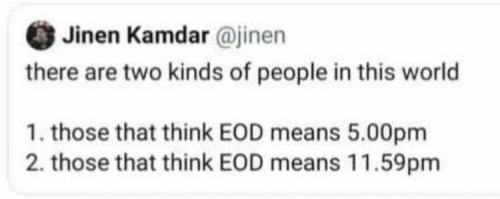
There are Two kinds of people in the world... 1. Those that think EOD means 5:00pm 2. those that think EOD means 11:59pm
There are Two kinds of people in the world… 1. Those that think EOD means 5:00pm 2. those that think EOD means 11:59pm

Which one do you fall under? I actually fall under neither because for me EOD is when I sign off for the day which is usually about 1am-2am depending, as when I say EOD I mean my End of Day i.e. when I log off for the day/night.

– Suramya

May 22, 2023

How not to do Interview Screening: Take 1000

Filed under: Humor,My Thoughts — Suramya @ 9:05 PM

Interviewing people is hard and each of us has their own bag of tricks and filters we use to identify the correct candidate for the position. However, some of the ways that people use to filter out applicants just make you go ‘Wow!’ with a head shake. One such example is below:

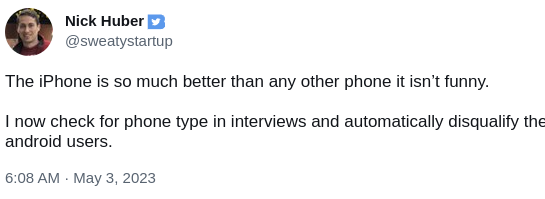
The iPhone is so much better than any other phone it isn't funny. I now check for phone type in interviews and automatically disqualify the Android Users
The iPhone is so much better than any other phone it isn’t funny. I now check for phone type in interviews and automatically disqualify the Android Users

Using a phone preference as a filter is not the right way to filter out candidates, if this becomes the norm then folks will start filtering candidates on what music they like, what brands they wear or what car they drive. Unless you are working at apple rejecting people for using an Android phone (which for the record is way better then iPhone) is foolish. It is also extremely classist, it automatically filters out people who can’t afford to buy an expensive iPhone as the General cost range for an iPhone is between $500 – $1,500+ whereas an Android phone would range between $100-$1,750+. It also filters out people who care about compatibility of their phone with other users at their home as it is hard to connect an iPhone to an Android ecosystem.

Plus it tells me that you are more concerned about arbitrary markers of evaluation than actually relevant criteria. Personally, I think that if the person interviewing me is using something like this as a filtering mechanism then I am better off getting rejected as who know what insane criteria they might come up with for performance evaluation once you join and start working with them.

I do have a lot of thoughts on interview processes and how some companies do screening but that is a post for another time.

– Suramya

May 19, 2023

KeePass exploit helps retrieve cleartext master password – Fix ETA July 2023

Filed under: Computer Security,My Thoughts,Tech Related — Suramya @ 8:06 PM

Security is hard to do and no matter how careful you are while coding every software will have bugs in it and some of these bugs have major security implications. Keepass which is a very popular password manager is vulnerable to extracting the master password from the application’s memory, allowing attackers who compromise a device to retrieve the password even with the database is locked. The bug is being tracked as CVE-2023-32784.

The issue was discovered by a security researcher known as ‘vdohney’ who has unfortunately also published PoC code that exploits the vulnerability called the “KeePass Master Password Dumper” on GitHub.

KeePass Master Password Dumper is a simple proof-of-concept tool used to dump the master password from KeePass’s memory. Apart from the first password character, it is mostly able to recover the password in plaintext. No code execution on the target system is required, just a memory dump. It doesn’t matter where the memory comes from – can be the process dump, swap file (pagefile.sys), hibernation file (hiberfil.sys), various crash dumps or RAM dump of the entire system. It doesn’t matter whether or not the workspace is locked. It is also possible to dump the password from RAM after KeePass is no longer running, although the chance of that working goes down with the time it’s been since then.

Tested with KeePass 2.53.1 on Windows (English) and KeePass 2.47 on Debian (keepass2 package). PoC might have issues with different encodings (languages), but that’s not confirmed as of now (see issue #3). Should work for the macOS version as well. Unfortunately, enabling the Enter master key on secure desktop option doesn’t help in preventing the attack.

The attack does require either physical access to the system or the system would need to be infected with Malware that give an attacker remote access with the ability to perform thread dumps. They can also extract the password from the process dump, swap file (pagefile.sys), hibernation file (hiberfil.sys) or RAM dump of the entire system.

The fix for the problem is in the works and the initial testing looks promising. Personally I think that the security researcher should have waited to release the PoC code till the fix is available but to each their own I guess.

Source: Bleepingcomputer.com: KeePass exploit helps retrieve cleartext master password, fix coming soon

April 14, 2023

My app that autoposts to Twitter has been suspended from accessing the Twitter API

Filed under: My Thoughts,Tech Related,Website Updates — Suramya @ 5:44 PM

Yesterday I got an email from Twitter stating the following:

Hello,

This is a notice that your app – Suramya’s Blog – has been suspended from accessing the Twitter API.

Please visit developer.twitter.com to sign up to our new Free, Basic or Enterprise access tiers.

More information can be found on our developer community forums.
Regards,
Twitter Developer Platform

The email actually looks like a really bad phishing email as it has no formatting, doesn’t give any links etc and is just a plain auto-generated email. I almost deleted it as spam but then realized that it could be a notification sent because they are forcing folks to use the new plans. Today I logged in to the Developer account and I was expecting to have an option to select one of the tiers, click save (pay if I was insane and decided to pay) and would be done with it. But that is not the case. I was greeted with the following banner when I logged in:


This App has violated Twitter Rules and policies. As a result, it can no longer be accessed. For assistance, submit a support ticket.

It looks like they couldn’t figure out how to temp block users who need to select a tier before being allowed to continue so they decided to suspend the app instead using the same process as what they would do if the app was suspended for ‘violations of Twitter Rules and policies’. Which is quite amusing because the app been used 12 times in the last 2 months to autopost links to my posts here when I create them. I did use the same app for testing a Twitter export script that I wrote a few months ago but haven’t run it in a while, either.

There is no way for me to edit/choose a tier for my app and I have no interest is spending the time to create another app just to post something on Twitter which will get about 2-10 view on an average. (Usually on the lower end of the scale). This was pretty much the last remaining vestige of my posting on Twitter and I am fine with it not working anymore.. I rather spend that time doing something more productive like watching paint dry.

– Suramya

April 4, 2023

Mastodon is so much better than Twitter, except for its search capabilities

Filed under: My Thoughts,Tech Related — Suramya @ 5:14 PM

Twitter has been slowing becoming less and less useful for getting updates from people you follow. Even my ‘Following’ tab is now showing entries from people I don’t follow and not all posts from the folks I follow show up on their either. Don’t even get me started about the ‘For You’ section which is full of nonsense that I am not really interested in. I have mostly switched over to Mastodon for updates and I see way better engagement over there. My blog auto-posts to both Mastodon and Twitter (along with LinkedIn and Facebook), on Twitter I have 84 followers and 11 followers on Mastodon (I only started posting there in 2023). My Tweets usually get between 2-10 views each and maybe 1 tweet out of 50 will get a response or like. The same post on Mastodon gets a lot more engagement, there have been posts which have had 8-10 replies and multiple likes.

However, that being said one thing that Twitter has which is missing from Mastodon is the ability to search. Earlier today I saw an article on how Twitter seems to have blocked users from authenticating to other services using their SSO offerings. I wanted to learn more about it and tried searching for it on Mastodon, and didn’t get any results (I then tried searching using a hashtag but no luck there as well). So I switched to Twitter and did a search there and immediately I got a lot of results that gave more information on the topic. I am sure that this event is being discussed in Mastodon but it is almost impossible to find because of the way the search is designed.

There is an opt-in project that allows people to opt-in to their setup to allow them to index your toots but because of the ‘amazing’ search in Mastodon, I can’t find the link to the project. 🙁 There are people working on this problem but a extremely vocal minority is hellbent against allowing people to search on Mastodon because they don’t want it. To be fair there are a lot of technical challenges in indexing all the toots across all the instances but it is not an insurmountable problem. It just needs people to look into the problem and others to let them work on the solution.

– Suramya

March 18, 2023

Scientists create a working supersolid in the lab

Filed under: Emerging Tech,My Thoughts — Suramya @ 11:34 PM

It seems that every year we learn more about the universe that makes the basic physics that we learned in school inaccurate or rather puts a lot of caveats in to the theories. Originally we had 3 states of matter: Solid, liquid and gas. Then came things like superfluids, Bose–Einstein condensates, quantum spin liquid, supercritical fluid, quark–gluon plasma, Rydberg polaron, and so many more weird possibilities. Last week, scientists from Innsbruck University in Austria have managed to create a new state of matter in 2D called Supersolids. Till now the researchers had only been able to create a 1D (a few molecules long) chain of SuperSolids but using cutting edge research they were able to create a 2D ‘paper’ of supersolid.

If you are like me, by now you will be wondering what on earth is a supersolid… Basically it is a state of matter that incorporates two different states of matter at the same time i.e. it is a solid as well as a superfluid at the same time. This gives it the ability to be a solid and still flow like a liquid without any friction at the same time. If that sounds confusing it is so because we are talking about Quantum effects which seem to exist in a state of constant contradiction and confusion (At least for me, when I try to understand them).

“To picture a supersolid, consider an ice cube immersed in liquid water, with frictionless flow of the water through the cube,” wrote Bruno Labruthe-Tolra, a physicist at Sorbonne Paris North University.

So, to create a supersolid, you first trap some atoms, then cool them, then play with their interactions. “If you tune those correctly, and you tune the shape of the trap correctly, you can get a supersolid,” says Norcia, the lead author.

Using this method, in 2019, researchers began to create a basic, one-dimensional supersolid: essentially, a thin supersolid tube in a straight line.

That’s what Norcia and his colleagues at Innsbruck University and the Austrian Academy of Sciences have now done. By tinkering with the device they used to trap atoms and the process they used to condense the atoms, they were able to extend their supersolid from one dimension into two: from a tiny tube into a small sheet.

There are a lot of interesting usecases for this technology when it matures, we could use it for lubrication in industrial machinery, create frictionless surfaces for tests. It could even be used in vacuum as is for various usecases. But that is still quite a way off because the work to go from 2D to 3D has just started and is still in the pre-research stage. However, while that is going on we do have a superSolid paper available for study while will give us more insight into this fascinating new substance.

The research has been published in Nature: Supersolids go two-dimensional

Source: Popsci.com: We finally have a working supersolid. Here’s why that matters.

– Suramya

« Newer PostsOlder Posts »

Powered by WordPress