Suramya's Blog : Welcome to my crazy life…

March 11, 2023

Thoughts about a list explaining how Linux users are characterized by these properties

Filed under: Linux/Unix Related,My Thoughts — Suramya @ 10:44 PM

It is always amusing to me when I read these lists that claim to characterize people, in this case while I was researching about companies acquired by Microsoft I ended up at Rational Wiki: OS Wars section where there is a section that claims that “Linux users are characterized by the following properties: I found it amusing so I am going to list them out here with my comments and thoughts about each of them.

An unhealthy desire to recompile the kernel at every opportunity.

[ST] Compiling a kernel was something that we had to do in Linux back in early 2000’s, but even then I never really had to compile the kernel to get things to work. I did do it to understand the process, but was never forced to do so. In fact I can’t remember the last time I had to compile the kernel on my system.

A disdain for newcomers who don’t know how to recompile the kernel.
Constantly rebuilding their machines because a kernel recompile failed.

[ST] Since I never had to compile it, I don’t expect others to do so. If you want to do it then its your prerogative but I don’t care one way or another.

Thinking those who don’t compile on their own computers or don’t use shell scripts and terminals on a daily basis are not real Linux users.

[ST] Unfortunately, there are idiots who think this, and attempt to gatekeep others and put them down just because they don’t use the ‘proper tools’/command line etc. I did write about this earlier: Stop hating on people because they don’t use the same tools as you because everyone has a different way of working and what works for you might not work for them and vice-versa. For example, I really dislike video tutorials and prefer text but I know plenty of folks who like video because it shows them what to do instead of having them imagine it. There is no one true way…

Constantly having incidents reported for not being in the sudoers file, but not being sure who they’re being reported to.

[ST] I don’t have incidents being reported constantly but did have to look up where the incidents are reported, which as expected was in the log files that an admin/root can audit.

Believing vowels are over rated, especially when it comes to naming important programs you expect to use every day.

[ST] Nope. I like my program names to be descriptive and really dislike SMS talk.

Cursing at Mac users for the number of shiny devices they can connect their computers to.

[ST] Again a nope. I can connect more things to my Linux machine and have them work off the bat than I could on a Mac. Sure some of the software is more polished on a Mac but from a connectivity perspective my Linux machine can connect to pretty much anything (sometimes a bit of tinkering might be required).

Either cursing that they need root, or cursing because they ran something as root that they really shouldn’t have.

[ST] Had this issue only when I was first starting out. After a little while things become automatic, if I run a root command as a non-root user, I just have to prepend sudo to it (or copy it to the root terminal). Accidentally running a command as root on the other hand is a much bigger issue. Haven’t done it in a while now but it is something to be careful of. I set the prompt to let me know what machine I am connected to and as what user so it makes it easier to spot if you are in the wrong window.

Believing a windowing system is a very clever way of having lots of command lines on screen at the same time. Like screen only less clever.

[ST] I really don’t get people who think like this and unfortunately there are folks who are like this. They think they are cleverer than everyone else and love putting others down.

Arguing with each other over which distribution to use.
Arguing with BSD users over their OS of choice.

[ST] This is a fight that I still see every once in a while but things have calmed down quite a bit from the earlier days where a question about which is the best distribution would ignite a flame war.

Arguing over whether to use a GUI or command line.

A lot of people think that using a command line makes you superior to other users, I think that you should use whatever works best for you at that point in time for the task you are doing. For example, if I am editing a video or sorting images I will prefer to use a GUI but for other tasks I prefer using the commandline. At the end of the day the idea is to get the work done, not argue about what is the best interface to do the work in.

Arguing about whether Emacs or vi is better. (Obviously vi is way better. No question. Unless you’re Richard Stallman or another member of the Church of Emacs.)

[ST] I prefer vi because it is installed by default on all Linux systems so if I ever have to recover from a crashed system I have an editor that I can use to edit files. Emacs is fine but I prefer vi / Notepad++ / kwrite for general editing.

Arguing about which language is the best for writing scripts (essentially the modern-day equivalent of the Tcl Wars between Tcl and GNU Guile’s implementation of Scheme).

[ST] I have no idea about the TCL wars and don’t really care what language you use for writing scripts. I have written scripts in Bash, Perl and Python for the automation and scripting I had to do and the language was chosen based on 1) What I was trying to do and how complicated the logic was 2) If I was trying to learn a new language the script was written in that language.

Complaining that we’re calling it Linux and not GNU/Linux.
Interjecting for a moment to explain why it’s actually GNU/Linux
Complaining that we’re calling it Open Source and not Free Software.

[ST] Complaining about the fact that someone calls it Linux and not GNU/Linux is just annoying and doesn’t make you look knowledgeable it makes you annoying. Technically they are correct but Linux is the expected usage and no, I am not about to start calling it GNU Linux just because some idiot thinks I should do so.

Constantly complaining about virtually all sorts of random, obscure problems such as their computer randomly shutting itself off at 9 pm on Mondays.

[ST] This is not just Linux users, any person who is a power user will face these kinds of issues and will ask around on how to fix them. General users will just get the helpdesk to come fix their systems for them.

Complaining that this list is not indexed from 0.

No, I don’t number my lists from 0. Just because Arrays are indexed from 0 doesn’t mean that I have to number everything starting from 0. However, I do prefer that the ground floor (1st floor in the US) be called the 0th Floor (or G Floor) instead of 1st floor like they do in the US because that’s how they do it in the rest of the world.

Believing that time started on January 1970.

🙂 No comments 🙂

Being able to understand this list.

Ha ha… I think any person actively working with computers like a sysadmin/programmer would understand this list.

I think the list should be updated but it did make me smile so I guess that is a win 🙂

– Suramya
March 7, 2023

What not to do when laying off people

Filed under: My Thoughts — Suramya @ 11:59 PM

Elon Musk drama seems to be almost impossible to avoid now since he has taken over Twitter, if it is not one thing it is another. Personally I feel that he has bought Twitter and can do whatever he wants with it whether the rest of us like it or not. He has been firing people pretty much since he took over, last week was the most recent batch where ~200 folks were laid off.

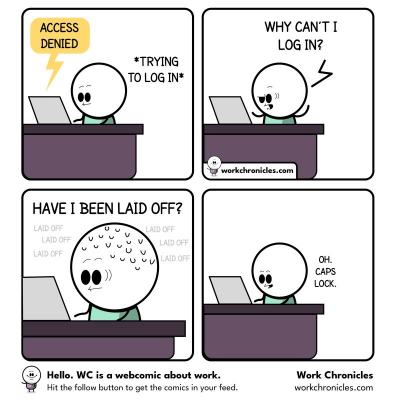
What is interesting and super unprofessional is that it looks like the folks who were laid off didn’t get an official notice that they have been terminated, instead their access just stopped working one day. Haraldur Thorleifsson, who was a senior director at Twitter was one of the folks impacted by this, so they reached out to HR at Twitter who didn’t (or maybe couldn’t) answer the simple question “Please confirm if I am an employee or not?”. After 9 days of getting nowhere, he posted a public thread on Twitter tagging Musk asking if he was laid off.

Dear @elonmusk

9 days ago the access to my work computer was cut, along with about 200 other Twitter employees.

However your head of HR is not able to confirm if I am an employee or not. You’ve not answered my emails.

Maybe if enough people retweet you’ll answer me here?

Elon was as ‘classy’ as ever and with jokes, silly emojies and then publicly mocked their disability, insinuated that they exaggerated their disability and saying they “did no actual work.”.

It is his right to fire people, but there is a right way and a wrong way to do it and this is definitely the latter. When Vinit was running his own company and had to lay off people because of funding issues, he did it in a fantastic way (See below) and I have seen other folks do the same thing.

Four years after he started Buildkar.com, a website for construction materials, Vinit Bhansali realised with horror that he had lay off eight employees. “It’s hard to tell your team you have to let them go. So, I reached out to everyone I knew — old friends from school, investors, acquaintances in the startup space — to find them jobs. Even VCs who had chosen not to invest in my company helped out and shared the resumes with startups in their portfolio,” he says. Eventually all eight were placed.

I have been part of companies that laid off employees and it was a painful experience even for those of us who weren’t laid off. All of us leveraged our connections to connect the folks impacted with teams that were hiring, a quick search on Mastodon/Twitter will get you links and posts from folks who don’t even know the folks impacted reaching out to help in anyway they can. That is humanity, that is how a person should behave.

This way of firing where a person doesn’t even know for sure they are fired or not is the worst way to fire someone, ghosting an employee is not a mature/professional way to do this. Imagine the stress an employee goes through if they are not able to log in even once due to a mistyped password or other technical issues. Then you have the uncertainty of not knowing if you are still employed and can afford to pay rent, buy groceries etc. For Musk its all a big joke because he never had to deal with not being able to afford food or have to worry about the rent being late but for most of the others people in his company they do have to worry about this along with a whole other set of responsibilities.


Have I been laid off?

The worst part is that a lot of people don’t see anything wrong with this. They still think he is the greatest thing to happen for mankind where in reality he is just another narcissistic billionaire who has gone back on pretty much every promise he ever made.

– Suramya

March 1, 2023

Don’t burn bridges by behaving unprofessionally when you leave a company

Filed under: My Thoughts — Suramya @ 4:47 PM

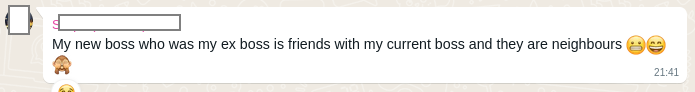
The message screenshot below was shared by a friend who is changing jobs. It is a perfect example for why you shouldn’t burn bridges when you leave a job because you never know who that person might be connected with and they just might end up sharing what you did when you quit ensuring that you don’t get that offer.

My new boss who was my ex boss is friends with my current boss and they are neighbours
My new boss who was my ex boss is friends with my current boss and they are neighbours 😬😄🙈

It is highly tempting to vent, curse or blast your manager/seniors/company when you leave or post nasty comments in public about it but you should please refrain. There was a case back in 2017 where a US flight attendant Steven Slater spectacularly quit his job aboard a JetBlue flight by grabbing a few beers, cursing out the airline on the AP and slipping down the plane’s emergency slide. This got him instant fame and spotlight and lots of people were applauding him on how he ‘had the guts’ to tell the truth and leave in an epic fashion. But this ‘epic’ resignation cost him his job, he was charged with criminal mischief, reckless endangerment and criminal trespass and had to pay a $10k fine. He can no longer work in the airline industry because no one wants to hire him and I don’t blame them. What is the guarantee that he wouldn’t pull a stunt like this again?

There was a case where a person was being interviewed for a job at one of my old companies and one of the hiring managers was talking about the candidate to a co-worker who had worked with the candidate before and commented that the person had behaved extremely unprofessionally with their boss on their last day because they were no longer reporting to him. The hiring manager discussed this with their manager and the decision was made to drop the candidate from consideration. It is a small world and you never know where you might cross paths with a person again down the line.

This is not to say that you shouldn’t respond to inappropriate behavior or actions. You can do that in a dignified/professional way like reporting to HR, putting in an official complaint etc. Or you can do it in an unprofessional way by cursing them out or posting a profanity ridden comment about them on their linkedIn page. See the difference? If you chose the first option, you might get asked about it during the interview and in the latter case you would just get dropped from consideration.

What do you think?

– Suramya

February 28, 2023

You shouldn’t spend money teaching folks how to survive in your toxic work culture, instead fix the Toxic culture

Filed under: My Thoughts — Suramya @ 5:39 PM

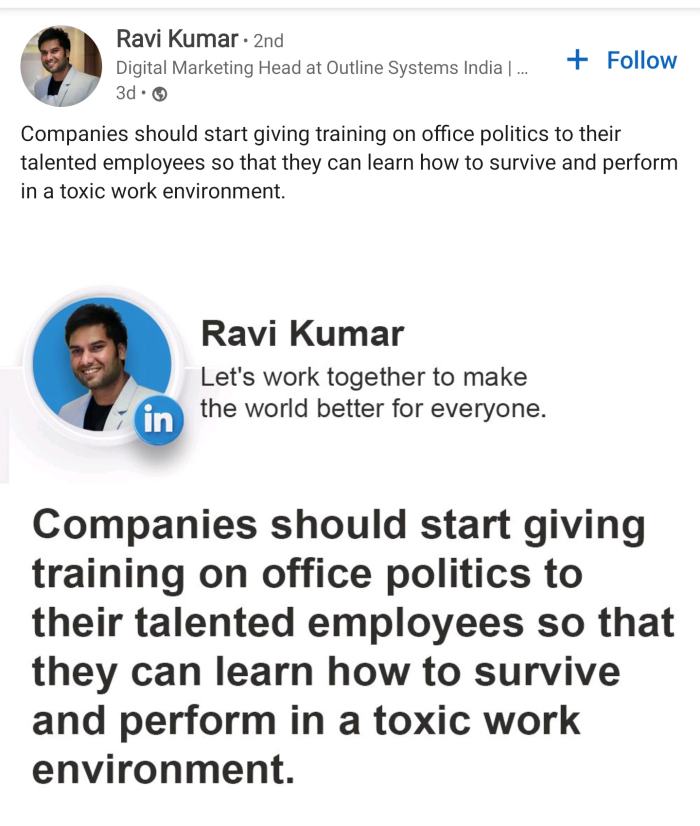
The following post showed up on my LinkedIn feed earlier today, it wants companies to put in time, effort & money to train employees on office politics so that they learn to survive and perform in a toxic work environment…


Personally, I would rather that the company spent all the effort to remove the toxicity from their work culture so that people don’t have to deal with it. This is like saying that we know that the water you drink is toxic, but we are not going to fix the root cause but will give you free chemo-therapy to mitigate your cancer.

If you run a company, and are hearing reports about toxic culture in the company then you need to address that immediately and not by giving people training on how to survive it, but rather by removing the toxic elements ruthlessly. Short term you might have to take a hit and might miss milestones or deliverables but long term your other employees who were just doing the bare minimum to get by would start engaging more, new talented folks would be happy to join your team/company because they wouldn’t get emails from friends telling them that it is a bad idea to join company X because of the toxic work environment.

What do you think?

– Suramya

February 27, 2023

It is now possible to put undetectable Backdoors in Machine Learning Models

Filed under: Computer Software,Emerging Tech,My Thoughts,Tech Related — Suramya @ 10:18 PM

Machine Learning (ML) has become the new go to buzzword in the Tech world in the last few years and everyone seems to be focusing on how they can include ML/AI in their products, regardless of whether it makes sense to include or not. One of the bigest dangers of this trend is that we are moving towards a future where an algorithm would have the power to make decisions that have real world impacts but due to the complexity it would be impossible to audit/check the system for errors/bugs, non-obvious biases or signs of manipulation etc. For example, we have had cases where the wrong person was identified as a fugitive and arrested because an AI/ML system claimed that they matched the suspect. Others have used ML to try to predict crimes with really low accuracy but people take it as gospel because the computer said so…

With ML models becoming more and more popular there is also more research on how these models are vulnerable to attacks. In December 2022 researchers (Shafi Goldwasser, Michael P. Kim, Vinod Vaikuntanathan and Or Zamir) from UC Berkely, MIT and Princeton published a paper titled “Planting Undetectable Backdoors in Machine Learning Models” in the IEEE 63rd Annual Symposium on Foundations of Computer Science (FOCS) where they discuss how it would be possible to train a model in a way that it allowed an attacker to manipulate the results without being detected by any computationally-bounded observer.

Abstract: Given the computational cost and technical expertise required to train machine learning models, users may delegate the task of learning to a service provider. Delegation of learning has clear benefits, and at the same time raises serious concerns of trust. This work studies possible abuses of power by untrusted learners.We show how a malicious learner can plant an undetectable backdoor into a classifier. On the surface, such a backdoored classifier behaves normally, but in reality, the learner maintains a mechanism for changing the classification of any input, with only a slight perturbation. Importantly, without the appropriate “backdoor key,” the mechanism is hidden and cannot be detected by any computationally-bounded observer. We demonstrate two frameworks for planting undetectable backdoors, with incomparable guarantees.

First, we show how to plant a backdoor in any model, using digital signature schemes. The construction guarantees that given query access to the original model and the backdoored version, it is computationally infeasible to find even a single input where they differ. This property implies that the backdoored model has generalization error comparable with the original model. Moreover, even if the distinguisher can request backdoored inputs of its choice, they cannot backdoor a new input­a property we call non-replicability.

Second, we demonstrate how to insert undetectable backdoors in models trained using the Random Fourier Features (RFF) learning paradigm (Rahimi, Recht; NeurIPS 2007). In this construction, undetectability holds against powerful white-box distinguishers: given a complete description of the network and the training data, no efficient distinguisher can guess whether the model is “clean” or contains a backdoor. The backdooring algorithm executes the RFF algorithm faithfully on the given training data, tampering only with its random coins. We prove this strong guarantee under the hardness of the Continuous Learning With Errors problem (Bruna, Regev, Song, Tang; STOC 2021). We show a similar white-box undetectable backdoor for random ReLU networks based on the hardness of Sparse PCA (Berthet, Rigollet; COLT 2013).

Our construction of undetectable backdoors also sheds light on the related issue of robustness to adversarial examples. In particular, by constructing undetectable backdoor for an “adversarially-robust” learning algorithm, we can produce a classifier that is indistinguishable from a robust classifier, but where every input has an adversarial example! In this way, the existence of undetectable backdoors represent a significant theoretical roadblock to certifying adversarial robustness.

Basically they are talking about having a ML model that works correctly most of the time but allows the attacker to manipulate the results if they want. One example use case would be something like the following: A bank uses a ML model to decide if they should give out a loan to an applicant and because they don’t want to be accused of being discriminatory they give it to folks to test and validate and the model comes back clean. However, unknown to the testers the model has been backdoored using the techniques in the paper above so the bank can modify the output in certain cases to deny the loan application even though they would have qualified. Since the model was tested and ‘proven’ to be without bias they are in the clear as the backdoor is pretty much undetectable.

Another possible attack vector is that a nation state funds a company that trains ML models and has them insert a covert backdoor in the model, then they have the ability to manipulate the output from the model without any trace. Imagine if this model was used to predict if the nation state was going to attack or not. Even if they were going to attack they could use the backdoor to fool the target into thinking that all was well.

Having a black box making such decisions is what I would call a “Bad Idea”. At least with the old (non-ML) algorithms we could audit the code to see if there were issues with ML that is not really possible and thus this becomes a bigger threat. There are a million other such scenarios that could be played and if we put blind trust in an AI/ML system then we are setting ourselves up for a disaster that we would never see coming.

Source: Schneier on Security: Putting Undetectable Backdoors in Machine Learning Models

– Suramya

February 1, 2023

Product Idea: Use ChatGPT to write movie/TV Tech Jargon dialogs

Filed under: Emerging Tech,My Thoughts,Tech Related — Suramya @ 3:00 AM

ChatGPT has taken the world by storm and everyday we hear more and more stories about how good it is and how it is changing the world. Personally I think the best description of the software is how Christine Lemmer-Webber put it:

ChatGPT is Mansplaining As A Service. A service that instantly generates vaguely plausible sounding yet totally fabricated and baseless lectures in an instant with unflagging confidence in its own correctness on any topic, without concern, regard or even awareness of the level of expertise of its audience.

People are using it for anything and everything including writing exams, writing articles, job posts, etc etc. While the result we get looks quite plausible there have been multiple cases where the output is subtly wrong and using the result as is can cause problems. However, there is one place that I can think of that ChatGPT would be extremely useful without any major drawbacks. If you have seen any TV show recently there are a lot of times where the characters will use technobabble to explain something and a lot of times the explanations are so ridiculous that they end up distracting you from the actual plot (such as it is).

My idea is that we encourage the writers to start using ChatGPT to write the jargon, even if it gets it wrong it wouldn’t be worse than what we have already so it is a win win. Plus since we all know that media tech works differently we don’t have to worry about the results being 100% accurate or correct.

One example is as below:

Forensic Scientist 1: Hey, have you seen the results from the trace DNA sample we collected from the crime scene?
Forensic Scientist 2: Not yet, I was just about to head over to the lab and check. Why, did you already receive them?
Forensic Scientist 1: Yeah, I just got an email from the lab. They’re pretty clear cut.
Forensic Scientist 2: Great, let’s take a look. What do the results show?
Forensic Scientist 1: Well, the sample is a match with the reference sample from our suspect. The lab confirmed a positive identification.
Forensic Scientist 2: That’s fantastic. Did they provide any details on the genetic markers?
Forensic Scientist 1: Yes, they identified several short tandem repeat markers that match between the sample and the reference. They also ran a mitochondrial DNA analysis and got a match there too.
Forensic Scientist 2: This is really strong evidence. But we need to be sure to double check all the details, especially since this is a high-profile case.
Forensic Scientist 1: Absolutely. I was thinking we should do a full review of the lab’s methodology and verify that the samples were handled and stored properly.
Forensic Scientist 2: That’s a great idea. Let’s also review the lab’s accreditation and see if they meet all the necessary standards.
Forensic Scientist 1: Right, we want to make sure our evidence is solid and can stand up in court.
Forensic Scientist 2: Definitely. Well, let’s head over to the lab and start our review.
Forensic Scientist 1: Sounds good. Let’s do it.

Another example:

Cybersecurity Professional 1: Hey, have you seen the alert about the recent cyberattack?
Cybersecurity Professional 2: Yes, I just received the notification. What do we know so far?
Cybersecurity Professional 1: The attack appears to be a phishing campaign. The attackers are using fake emails to steal login credentials from unsuspecting victims.
Cybersecurity Professional 2: That’s a common tactic. Did they manage to compromise any systems?
Cybersecurity Professional 1: Yes, we have reports of several systems being breached. Our incident response team is currently investigating the extent of the damage.
Cybersecurity Professional 2: Okay, let’s see if we can help with the investigation. What’s the first step?
Cybersecurity Professional 1: First, we need to isolate the infected systems and contain the spread of the attack. Then we can start looking into how the attackers gained access and what they did once they were in.
Cybersecurity Professional 2: Right. I’ll start working on the containment and isolation. Have you seen any indications of what the attackers are after?
Cybersecurity Professional 1: It’s not clear yet, but it looks like they are targeting sensitive information, such as financial data and personal information. We need to be proactive and make sure all our systems and data are secure.
Cybersecurity Professional 2: Agreed. We need to inform the relevant stakeholders about the attack and what measures we’re taking to prevent further damage.
Cybersecurity Professional 1: Absolutely. We also need to start preparing for the worst-case scenario, in case the attackers managed to exfiltrate any data.
Cybersecurity Professional 2: That’s a good point. We need to be prepared for the aftermath and make sure we have a plan in place to respond effectively.
Cybersecurity Professional 1: Right. Let’s get to work and make sure we minimize the impact of this attack.

What do you think?

– Suramya

January 25, 2023

Fewer than 50% of smart appliances are connected to the internet by users and that percentage is too high

Filed under: My Thoughts,Tech Related — Suramya @ 3:04 AM

Smart Appliances or Smart Devices are a pain. Yes, sometimes they make your life easier by allowing you to control your lighting from the bed or switch on your devices remotely but they cause major security problems. There is a term for these ‘smart’ devices: “Internet of Shit”. This refers to all the devices that are connected to the internet that have no business being connected to it. One example is an IoT enabled toilet, Smart Toaster, Smart Mirror etc etc.

There are a lot of potential issues in IoT devices including but not limited to:

  • If the manufacturer decides to shut down the service the device becomes an expensive paperweight
    • Older model Lexus cars lost all remote capabilities because the 3G towers it depended on shut down
    • Older Sonos speakers lost functionality when the company decided to decommission them
    • Tesla car bricked itself because it lost connectivity after owner parked it in a basement.
  • Need a 24×7 active connection
    • People got locked out of their house because a server upgrade was happening
    • During an AWS outage folks were unable to change the temperature using their NEST systems
  • Security Issues: IoT devices are the amongst the most insecure devices out there
  • Lack of Interoperability

and much more. When I bought my AC a couple of years ago I had to argue for a good 15 mins to get a non-smart/internet connected AC. The salesperson couldn’t digest why I wasn’t interested in having a smart AC. A few years later I got a washing machine and there was no option to get a dumb machine, but thankfully it has the option to create a local hotspot that I can connect to from my phone to control the machine. Yeah, it would be more convenient to do it from a distance but guess what I am already next to the machine when I am putting clothes for a wash and it is not that hard to connect to the local AP, start the cycle and then switch back.

A lot of appliance manufacturers bet big on the Smart revolution and according to recent studies are quite surprised to find out that fewer than 50% of their consumers actually connect their smart devices to the internet. The main reason behind it, in my opinion is that there is no major value add for a toaster or a fridge or a toilet to be connected to the internet.

This whole conversation reminded me of the following quote:

Tech enthusiasts: My entire house is smart. Tech workers: The only piece of technology in my house is a printer and I keep a gun next to it so I can shoot it if it makes a noise I don’t recognize.

I am not as bad but nothing at my house is connected to the internet if it doesn’t need to be and then also it is on a separate network isolated from my home machine.

Source: Slashdot: Appliance Makers Sad That 50% of Customers Won’t Connect Smart Appliances

– Suramya

January 22, 2023

Working remotely doesn’t leads to lonely people no matter what folks on Twitter say

Filed under: My Thoughts — Suramya @ 1:11 AM

“100% remote work combined with a no meeting culture is going to create a large group of lonely, isolated workers”Alex Cohen posted this on Twitter a little while ago. Apparently the only way to ward off loneliness is to work in an office and attend meetings since having friends and spending time with them is obviously so last millennium.

I am someone who tends to be a little on the workoholic side if I am not careful. I have spent all weekend in office multiple times and one of my managers frequently used to message me asking me why I was still online at 3am and logged into office systems. That being said, there is more to life than work. In one of our Townhalls in a previous organization, someone asked the CEO a question “What are you doing to ensure employees have a proper work-life balance” and he responded (and I am paraphrasing since this was a while ago) “It is not my or the company’s responsibility to ensure you have a proper work-life balance. Only you know what balance would work for you and you need to tell us when you have enough work and need to stop for a break. If you allow/want we can give you work 24 hours a day 7 days a week because we have enough things to do. You need to be the one to decide what work-life balance means for you and then let us know. Then we will ensure that you get to follow that.” This stuck with me since I heard it and I quote it often with my reportees when we talk about Work-life balance.

This is not to say that you shouldn’t make friends at work or people objecting to the statement don’t enjoy working with others on a project. However, if you make your work the defining factor in your life, you are going to burn out. (Telling from experience) It is good to step away from work to do something else as that will rejuvenate you and might even give you a new perspective. For me I read books, go hiking and travel to get a break from work. You will not believe how many of my project ideas and fixes for issues I was facing were conceptualized while I was slogging away on a hilltop or driving to a new location for a trip.

Someone once told me that it is ok to love your job but don’t expect that love to be always returned. One recent example is the Microsoft Engineer who spent 21 years with MS as a great performer but was still fired earlier this week with little notice. There are multiple such stories and I could fill books with various similar examples.

I have been working remotely since 2020 and it does get tiring as I can’t meet folks face to face for discussions and I do miss the coffee breaks and the random discussions. However, once I log off from work I spend time with family, I go out with friends, I watch movies and do other things and guess what I am happy. Work is one aspect of my life and while it is an important part it doesn’t necessarily define who I am as a person.

When I was a kid I complained to my dad that I was bored and he responded that the fact that you are bored is your problem, you need to figure out how to keep yourself entertained because it is not the job of others around you to keep you entertained. So after that me and my sister would come up with things to keep us busy and entertained. The same concept applies to feeling lonely, it is not the job of others in your life to keep you from feeling lonely (they will obviously be there for you) but rather you need to reach out to them and make connections and do things that would keep you entertained & connected.

What do you think?

– Suramya

January 15, 2023

Calling something older than Christianity doesn’t actually show that it is super old

Filed under: My Thoughts — Suramya @ 11:59 PM

I was reading Agents of Light and Darkness by Simon R. Green and came across this quote “Dedicated to the patron saint of lost causes, St. Jude’s is an old, old place; a cold stone structure possibly older even than Christianity itself.” in the book and it made me laugh. A lot of books have this habit of stating that xyz is older than Christianity as the measurement of how old things are and whenever I read it I just have to say that Christianity only started ~2000 years ago which is not that old compared to older religions, structures and things that exist in the world.

For example, Pyramids of Giza were built over 4500 years ago, a shrine worshiping Goddess (Shakti) made of stone at Baghor, Madhya Pradesh is dated 9000–8000 BC, Megalithic Temples in Malta are between 3000 and 700 BC. Even if you talk about religion Hinduism was started way back in 7,000 BCE, Zoroastrianism was founded ~1600 BCE and Confucianism, Buddhism & Jainism all were founded ~600 BCE. (Source: Oldest Religions in the world) There are so many things, places and ideas that are older than Christianity but there is a certain group of people in the world for whom the world doesn’t seem to exist before its start.

If you want to talk about old things, you can say that it is older than the discovery of fire or older than the start of agriculture or something similar and that still makes some sense. 2000 years is just a blink of an eye and even though it is a popular religion, measuring the age of something against it just doesn’t make sense to me.

– Suramya

January 14, 2023

Manager upset about order of recipients in email

Filed under: My Thoughts — Suramya @ 9:38 PM

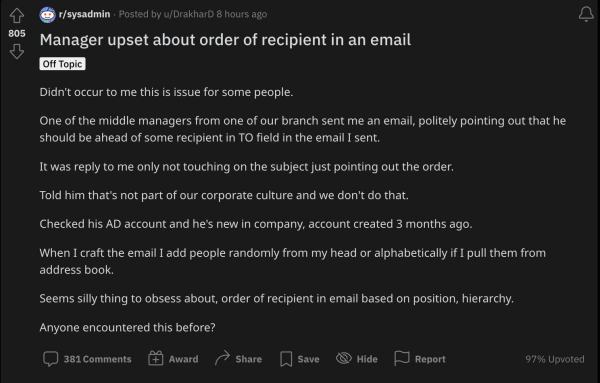
There are a lot of people who are really concerned about their power & position, and will go to any lengths to ensure that everyone around them knows how powerful/senior they are. The below screenshot came up in one of my feeds a while ago and I found it to be really funny and all together ridiculous.

Didn't occur to me this is issue for some people.

One of the middle managers from one of our branch sent me an email, politely pointing out that he should be ahead of some recipient in TO field in the email I sent.

It was reply to me only not touching on the subject just pointing out the order.

Told him that's not part of our corporate culture and we don't do that.

Checked his AD account and he's new in company, account created 3 months ago.

When I craft the email I add people randomly from my head or alphabetically if I pull them from address book.

Seems silly thing to obsess about, order of recipient in email based on position, hierarchy.

Anyone encountered this before?
Manager upset about order of recipient in an email

What is even more funny is that people with actual power/position will not pull nonsense like this because they don’t need to. It’s only people who have little power who want to pretend that they have a lot. I have had the unfortunate ‘pleasure’ of dealing with some of these folks and it is always a massive pain because their ego will take any thing as an offense against them and will react accordingly to put the person in place. The only thing these folks will give any notice to is the people above them in power and for them they will do anything and everything to keep them happy.

This is one of the sillier examples that I have heard. Personally, I choose the email addresses in the order I remember them, starting with the main people (the people to whom the email is addressed) followed by the people who need to know what I am talking about in the email. I remember reading somewhere that folks in business schools and one of the big 4 consulting firms actually train people in what order the email addresses need to be listed but I can’t find the reference now. I think that is just a waste of time and energy which the person sending the email should that time on something useful or just take a short break instead of this nonsense.

I do remember having been called out for putting one of the senior people in the CC field instead of the To field even though they were just copied as a courtesy to keep them aware of what was going on. Going forward I remembered putting them in the To field but always found it silly. For me the To field is for the people the mail is addressed to or the people who need to action something on the email, the rest go into the CC field. For emails sent to me (I am in the To field), I have a rule that marked emails where I was in the To field in a specific color so that I knew those were emails I might need to action and that has worked great for me in combination to all my other email rules.

What do you think? Does the order of names in the email matter?

– Suramya

« Newer PostsOlder Posts »

Powered by WordPress