Suramya's Blog : Welcome to my crazy life…

May 2, 2022

MIT researchers create a portable desalination unit that can run off a single solar panel

Filed under: Emerging Tech,My Thoughts,Science Related — Suramya @ 2:33 AM

The lack of drinking water is a major problem across large portions of the world and over 2 billion people live in water-stressed countries. According to WHO at least 2 billion people use a drinking water source contaminated with feces. On the other side, places near the sea have to deal with salt water contamination of their drinking supply. If we can desalinize sea water cheaply and easily then it will be a great boon to world.

There are existing technologies that convert sea-water to drinking water but they require massive energy supply and large scale plants which are very expensive to make. To resolve this issue MIT researchers have been working on creating a portable desalination unit that generates clear, clean drinking water without the need for filters or high-pressure pumps. Since the unit doesn’t use filters or high-pressure pumps the energy requirement is low enough that it can be run off a small, portable solar panel.

The research team of Jongyoon Han, Junghyo Yoon, a research scientist in RLE; Hyukjin J. Kwon, a former postdoc; SungKu Kang, a postdoc at Northeastern University; and Eric Brack of the U.S. Army Combat Capabilities Development Command (DEVCOM) created this and the initial prototype has worked as expected. Their research has been published online in Environmental Science and Technology.

Instead, their unit relies on a technique called ion concentration polarization (ICP), which was pioneered by Han’s group more than 10 years ago. Rather than filtering water, the ICP process applies an electrical field to membranes placed above and below a channel of water. The membranes repel positively or negatively charged particles — including salt molecules, bacteria, and viruses — as they flow past. The charged particles are funneled into a second stream of water that is eventually discharged.

The process removes both dissolved and suspended solids, allowing clean water to pass through the channel. Since it only requires a low-pressure pump, ICP uses less energy than other techniques.

But ICP does not always remove all the salts floating in the middle of the channel. So the researchers incorporated a second process, known as electrodialysis, to remove remaining salt ions.

Yoon and Kang used machine learning to find the ideal combination of ICP and electrodialysis modules. The optimal setup includes a two-stage ICP process, with water flowing through six modules in the first stage then through three in the second stage, followed by a single electrodialysis process. This minimized energy usage while ensuring the process remains self-cleaning.


Video demonstration of the process

The prototype device was tested at Boston’s Carson Beach and was found to generate drinking water at a rate of 0.3 liters per hour, requiring only 20 watts of power per liter during the use. As you can guess this is pretty amazing. If the device can be mass-produced it will help reduce the scarcity of drinking water in the world without requiring massive amounts of energy which would cause other climate impact.

One downside of this kind of machine is that it creates a byproduct of highly saline water as the salt from the pure water is mixed with the waste water. Releasing this water in the ocean has a huge impact on the sea life as the water suddenly becomes too saline for them. If the water is allowed to seep into the land then it will reduce the fertility of the soil due to the increased salt in the soil. In addition to making the device commercial we also need to do research on what we should do with the waste water generated so that the adverse impact of the product can be offset.

Source: MIT News: From seawater to drinking water, with the push of a button

– Suramya

May 1, 2022

Book Review: Eight Million Gods (Eight Million Gods Book 01) by Wen Spencer

Filed under: My Thoughts,Reviews-Urban Fantasy — Suramya @ 12:38 AM

Eight Million Gods (Eight Million Gods Book 01)

by Wen Spencer

Description:

First entry in a new urban fantasy saga by the creator of the popular Tinker contemporary fantasy/SF series. A young American expat writer in Japan suffering from OCD tries to figure out if she’s crazy or not while solving a murder that may be part of a war among Japanese deities.A contemporary fantasy of mystery and death as American expats battle Japanese gods and monsters to retrieve an ancient artifact that can destroy the world. On Saturday afternoon, Nikki Delany thought, “George Wilson, in the kitchen, with a blender.” By dinner, she had killed George and posted his gory murder to her blog. The next day, she put on her mourning clothes and went out to meet her best friend for lunch to discuss finding a replacement for her love interest. Nikki is a horror novelist. Her choice of career is dictated by an Obsessive Compulsive Disorder that forces her to write stories of death and destruction. She can’t control it, doesn’t understand it, but can use it to make money anywhere in the world. Currently “anywhere” is in Japan, hiding from her mother who sees Nikki’s OCD as proof she’s mentally unstable. Nikki’s fragile peace starts to fall apart when the police arrest her for the murder of an American expatriate. Someone killed him with a blender. Reality starts to unravel around Nikki. She’s attacked by a raccoon in a business suit. After a series of blackouts, she’s accompanied by a boy that no one else can see, a boy who claims to be a god. Is she really being pursued by Japanese myths – or is she simply going insane? What Nikki does know for sure is that the bodies are piling up, her mother has arrived in Japan to lock her up for the rest of her life – and her novels always end with everyone dead.

Buy From:

Rating:

Review:
This is another fantastic book by Wen Spencer and is pretty fast paced and easy to read. The main character Nikki has a OCD disorder that forces her to write constantly but everyone she writes about seem to die horrible deaths. She decides to channel this urge to write by becoming a famous horror writer under a pseudonym. It also allows her to avoid her mother who is very controlling and wants to get her committed to an insane asylum. A good part of how the character develops is due to the main character trying to figure things out without alerting her mother or involving the authorities.

The book is based in Japan and the locations & culture are well explained and described. Even though I have never been to Japan it was easy for me to imagine the city due to the fantastic descriptions. Plus the author managed to avoid stereotyping the culture which was a pleasant surprise and the explanations were enough to get me to look up additional details on the internet as I was reading the book.

Due to the fast paged action the book feels like it is a lot shorter than it is and the final ‘battle’ was a bit anti-climatic for my taste. It felt like there was a lot of buildup and then suddenly all was resolved. They could have expanded this section a little to justify the buildup, but that being said it was still a good conclusion and it has set the stage for future adventures so I am guessing there will be more books in the series down the line.

April 30, 2022

Thoughts on Star Trek: Picard’s Time Travel inconsistencies

Filed under: My Thoughts — Suramya @ 10:33 AM

The season 2 of Star Trek Picard is going on and while I like the season and enjoy looking at the characters in a different setting, the whole time travel thing and how they are ignoring the impact of what they are doing in the past is getting annoying.

There are going to be spoilers in this post about the latest episodes of the series. So if you haven’t seen the episode I suggest you stop reading now to avoid spoilers.

In the series, Picard and team are stuck back in the past and the Borg Queen has taken over Jurati and wants to get a 400 year jump on assimilating the galaxy. One point they ignore is why the queen doesn’t start with Assimilating Earth and then move to the other planets because that would give her a base of operations and allow them to expand into the Alpha quadrant without any competition, but lets put that aside for now. In the latest episode Seven is injured and apparently the only way to save her is for Jurati to strike a deal with the queen. Which is that the queen would fix Seven by giving her Borg implants back and Jurati will work with the queen.

She pitches the idea that they should assimilate the people who need help or are lonely instead of forcefully assimilating whole cultures and species, basically giving them a second chance. Instead of the famous “Resistance is Futile. We are the Borg. Lower your shields and surrender your ships. We will add your biological and technological distinctiveness to our own.” . The queen agrees so they both take the ship and fly off to the delta quadrant to assimilate people in a more compassionate way. But guess what, if Borg start doing compassionate assimilation 400 years in the past then it changes the whole history and the future would be drastically different. It literally changes the entire future of the delta quadrant as the Borg are not assimilating and killing off species, which means they do things differently. You can’t tell me that this will not create a whole new future because without the borg, there is no Seven of Nine (which means Voyager would probably not make it back), there is no Locutus, no Borg war and so many other changes.

The whole premise of ST Picard is that if Picard’s ancestor doesn’t go for the Europa mission the federation no longer exists and there is a Confederation of Earth that has destroyed / killed most of the species in the galaxy. This minor change causes such alteration of the future so it is hard to accept that letting the Borg Queen loose in the past will not have an impact.

There are so many other things that they do which should impact the future but apparently won’t because they are needed to further the plot. This is why I don’t like this kind of time travel series because they break their own rules about what is allowed and what is not.

I wonder how they will address the whole new timeline and all the impact they have caused. I just hope it wont be something silly like Q resetting the timeline to the original at the end of the season.

– Suramya

April 29, 2022

Malware in Windows: TPM Bypasses & Firmware level persistence

Malware is the short form for Malicious Software and is basically software that allows attackers to infect a computer system or device to steal information, disrupt operations or gain access to sensitive data. It is a general term that includes viruses, worms, trojans, spyware, rootkits etc. (Cisco, 2021)

Conceptually the foundations for creating malware were laid almost simultaneously with the creation of the first computers. In 1951, John von Neumann proposed methods on how to create self-replicating automata (Neumann, 1951) and a few years later in 1959 Lionel Penrose published his paper on ‘Self-Reproducing Machines’ this paper was used as the basis for creating replicating machine code that were the basis of the later generations of malware. In 1970’s the creeper virus infected the ARPANET (Milošević, 2013) followed shortly after by Rabbit (Milošević, 2013) which spread rapidly to computers and created copies of itself overloading the machine and impacting system performance. (Milošević, 2013)

In the 1986, the first malware called Brain.A that targeted the PC platform was released. (Milošević, 2013) It used floppy disks as the infection mechanism by infecting the boot sector of every floppy disk used in an infected computer. Other viruses of the time used similar mechanisms to propagate and were quite prevalent by the measures of the time. Once Microsoft Windows was released viruses were created that targeted the new operating system with WinVir being the first virus for the new operating system, it gained persistence by modifying the Windows Executable files. (Milošević, 2013) It spread to new systems over floppy disks.
For almost a decade, infected disks and CD’s remained the primary method of infection for computers. In 1998 this changed with the release of Happy99 in late 1998 that spread via email attachments. Another popular vector for virus infections was macro viruses that infected Microsoft word files which were shared frequently with other users allowing the virus to spread. With the increasing popularity of the Internet, the new malware created during this time leveraged the internet as a transmission vector.

In early 2000, Code Red worm was created that leveraged vulnerabilities in the IIS webservers to propagate. (Milošević, 2013) This opened a new infection vector where the malware would scan for and exploit systems running vulnerable software.

Over the years, malware has become more and more common and has evolved to gain persistence using multiple methods such as using rootkits to infect the OS kernel and other such methods. The one constant throughout the years was that we could clean up a malware infection by formatting the infected drive and restoring from a clean backup. As long as the backup and the installation media were clean we could be confident that the infection was cleared.

Unfortunately, this is no longer the case with new strains of malware using sophisticated techniques to gain persistence using the computer firmware.

A. UEFI malware – The early years

UEFI rootkits were referenced in various leaks and were considered mostly theoretical. The Hacking Team referenced something called ‘rkloader’ in their internal presentations and the Vault7 leaks referenced ‘DerStarke’ which was an EFI/UEFI boot implant. But there was no real evidence of these being used so they were considered mostly theoretical for the most part.

This changed in 2018 when the first rootkit that leveraged the UEFI to achieve persistence was discovered. This malware called Lojax was created by the Sednit APT group. It used a malicious UEFI module written into the SPI flash memory to ensure that it was able to execute malware during the boot up process. (ESET Research, 2018)

B. UEFI Malware – Infecting SPI flash memory

The LoJax malware used the kernel driver RwDrv.sys to access the UEFI settings. The driver is distributed with RWEverything, a freeware utility that can read the BIOS information in most computers. (ESET Research, 2018)

The malware used this driver to read the contents of the SPI flash memory into a file, by running a file called ReWriter_binary.exe. The data in the SPI is stored in volumes using the Firmware File System (FFS). It then parses the volues to search for the Ip4Dxe file. This file along with DXE Core is then modified to add the malicious UEFI module to it post which the entire file is written back to the SPI memory. If the configuration allows write access to SPI the malware immediately writes to the SPI memory but if write access is disabled it exploited a race condition vulnerability in the BIOS locking mechanism to bypass the write protection in SPI flash memory. (CERT, 2015)

C. MoonBounce: UEFI Bootkit

The MoonBounce Bootkit is the third instance of malware that uses UEFI to gain persistence, with Lojax and MosaicRegressor being the other two instances where it was used.

MoonBounce is a lot more sophisticated than the previous iterations and it executes completely in the system memory without writing anything to the hard drive making it a lot harder to detect than the previous iterations of the malware. It stages the execution and deployment of payloads over the internet allowing the attacker to deploy payloads on the system to achieve specific tasks.
MoonBounce was detected in spring 2021 and like the previous iterations attacks the DXE Core module in UEFI to infect the SPI Memory.

D. Using TPM Module & Trusted Computing to protect against this attack

The TPM Module in the modern machines is designed to provide hardware-based, security-related functions and allows the system to secure the system using integrated cryptographic keys.

If TPM is enabled and is being used correctly then it gives the system a way to ensure that all firmware and boot files are unmodified. If any of the files are modified then they will not pass the cryptographic check and the boot process will be halted. This would prevent the infected SPI memory from being loaded and would warn the defenders that their system has been breached.

Unfortunately, it is possible to disable the TPM chip for historical compatibility reasons, so the malware can do the same. One of the ways to disable the check and bypass the Secure Boot & TPM check is to modify the registry files in Windows. The steps to do so are very simple and are shown below (Tibbetts, 2021):

  • At the run prompt type in regedit, and press Enter.
  • Go to Computer\HKEY_LOCAL_MACHINE\SYSTEM\Setup
  • Right-click on Setup and click New > Key. Name that LabConfig
  • Click on LabConfig, then right-click on the right pane, and click New > DWORD (32-bit Value).
  • Name the entry as BypassTPMCheck and change its Value data to 1
  • Create two more DWORDS and change the Value data to 1 just like you did above and name them BypassRAMCheck and BypassSecureBootCheck.

This removes the check for Secure Boot and while it can be desired at times it does open up the system to risk so should only be used for specific use cases where no other option is available.

Protecting against malware using firmware level persistence

To protect against this threat, we need to ensure that all components of the operating system and software on the computer are patched and updated to the latest version. We should enable end-point monitoring and IDS on the network to detect infection attempts. This will allow us to detect the malware before it infects the system and block it pre-emptively. The internet and email gateways should scan all incoming files to detect and block malware. In addition to the standard precautions to protect against malware, we should also ensure that all systems on the network are running the latest version of the UEFI/BIOS available.

Unfortunately, the remediation of the security issues in UEFI is a hard problem and doesn’t have an easy solution. So, the best way to protect against the threat is to try to prevent the system from getting infected in the first place.

Another option to detect infected SPI Memory is to create a tool that periodically creates a dump of the SPI memory and compares the checksum of the dump with a known clean dump. If the values don’t match then there is a high probability that the memory is infected and the administrators can then take steps to clean the firmware by flashing it with a known clean version of the firmware.

With the new methods of persistence available to the malware writers the best way to protect the assets is to try to ensure that you prevent the infection from happening in the first place. Once the machine is infected the task becomes harder and we would need to spend extra time and effort to clean and restore the systems to a clean state.
Done correctly this will decrease the risk of data exfiltration but no technique to detect infection is perfect so a lot of review and audits need to be done on a periodic basis to ensure that the system is still secure.

References

CERT. (2015, January 5). CERT/CC Vulnerability note vu#766164. VU#766164 – Intel BIOS locking mechanism contains race condition that enables write protection bypass. Retrieved March 21, 2022, from https://www.kb.cert.org/vuls/id/766164

Cisco. (2021, July 30). What is malware? – definition and examples. Cisco. Retrieved March 21, 2022, from https://www.cisco.com/c/en_in/products/security/advanced-malware-protection/what-is-malware.html
ESET Research. (2018, October 9). Lojax: First UEFI rootkit found in the wild, courtesy of the Sednit Group. WeLiveSecurity. Retrieved March 21, 2022, from https://www.welivesecurity.com/2018/09/27/lojax-first-uefi-rootkit-found-wild-courtesy-sednit-group/

Neumann, J. V. (1951). Massachusetts Institute of Technology. Theory of Self Replicating Automata. Retrieved March 21, 2022, from https://cba.mit.edu/events/03.11.ASE/docs/VonNeumann.pdf
Tibbetts, T. (2021, July 10). How to bypass secure boot & trusted platform module. Providing Free and Editor Tested Software Downloads. Retrieved March 21, 2022, from https://www.majorgeeks.com/content/page/bypass_tpm.html.


This was a paper for my Class in Q1 2022 which is why it is more formal than my usual posts.

April 25, 2022

Rainbow Algorithm (one of the candidates for post-quantum Cryptography) can be broken in under 53 hours

Quantum Computing has the potential to make the current encryption algorithms obsolete once it gets around to actually being implemented on a large scale. But the Cryptographic experts in charge of such things have been working on Post Quantum Cryptography over the past few years to offset this risk. After three rounds they had narrowed down the public-key encryption and key-establishment algorithms to Classic McEliece, CRYSTALS-KYBER, NTRU, and SABER and te finalists for digital signatures are CRYSTALS-DILITHIUM, FALCON, and Rainbow.

Unfortunately for the Rainbow algorithm, Ward Beullens at IBM Research Zurich in Switzerland managed to find the corresponding secret key for a given Rainbow public key in 53 hours using a standard laptop. This would allow anyone with a laptop to ‘prove’ they were someone else by producing the secret key for a given public key.

The Rainbow signature scheme [8], proposed by Ding and Schmidt in 2005, is one of the oldest and most studied signature schemes in multivariate cryptography. Rainbow is based on the (unbalanced) Oil and Vinegar signature scheme [16, 11], which, for properly chosen parameters, has withstood all cryptanalysis since 1999. In the last decade, there has been a renewed interest in multivariate cryptography, because it is believed to resist attacks from quantum adversaries. The goal of this paper is to improve the cryptanalysis of Rainbow, which is an important objective because Rainbow is currently one of three finalist signature
schemes in the NIST Post-Quantum Cryptography standardization project.

This obviously disqualifies the algorithm from being standardised as it has a known easily exploitable weakness. It goes on to prove that cryptography is not easy and the only way to ‘prove’ the strength of an algorithm is to let others test them for vulnerabilities. Or as Bruce Schneier put it in Schneier’s Law: ‘Anyone can create an algorithm that they themselves can’t break.’ , you need others to validate that claim.

Paper: Breaking Rainbow Takes a Weekend on a Laptop by Ward Beullens (PDF)
Source: New Scientist: Encryption meant to protect against quantum hackers is easily cracked

– Suramya

April 23, 2022

Molecular engines made of protein could power molecular machines

Filed under: Emerging Tech,My Thoughts — Suramya @ 11:48 PM

Nano-machines have long been staples of Sci-Fi stories where nanotech is used to cure illnesses , make new materials, kill people etc etc and in the recent years a lot of effort has been put in to make these machines real. Basically speaking, a nanomachine, also called a nanite, is a mechanical or electromechanical device whose dimensions are measured in nanometers (millionths of a millimeter, or units of 10 -9 meter). [What is Nanite] They are still in the R&D phase but a lot of progress is being made in the field.

Researchers at the University of Washington in Seattle have created the first building blocks of a molecular engine, namely the axles and rotors. The really cool part is that these are self assembling and use custom designed new proteins unlike any found in nature. The researchers used the advances in Deep learning software to predict what shape a given DNA sequence will fold into making it easier to find a code that makes the desired shape. This allows them to create custom shapes without having to modify existing molecules which can be quite hard.

The team made the machine parts by putting DNA coding for the custom proteins into E. coli bacteria, and then checked their structure using a method called cryogenic electron microscopy.

This showed that the axles assembled correctly inside the rotors, and also revealed the different configurations that would be expected if the axles were turning. But because cryogenic electron microscopy can only provide a series of stills rather than a moving picture, the team can’t say for sure if the axles are rotating.

If they are, it would only be a random back-and-forth movement driven by molecules knocking into each other, a phenomenon called Brownian motion. The team is now designing more components to drive the motion in one direction and create a rotary engine, says Baker.

The work is still in the preliminary stage and the team is designing more components to drive the motion in one direction and create a rotary engine to make sure that the movement seen in the current trials is not just due to Brownian motion. Once the technology is perfected it has a lot of use cases in fields such as BioMed to remove tumors, clean out arterial blocks, repair injuries and fields like material design where these machines can be used to create new materials which are stronger and lighter.

Source: Tiny axles and rotors made of protein could drive molecular machines
Paper: Computational design of mechanically coupled axle-rotor protein assemblies

– Suramya

April 22, 2022

Implications and Impact of Quantum Computing on Existing Cryptography

As all of you are aware the ability to break encryption of sensitive data like financial systems, private correspondence, government systems in a timely fashion is the holy grail of computer espionage. With the current technology it is unfeasible to break the encryption in a reasonable timeframe. If the target is using a 256-bit key an attacker will need to try a max of 2256 possible combinations to brute-force it. This means that even with the fastest supercomputer in the world will take millions of years to try all the combinations (Nohe, 2019). The number of combinations required to crack the encryption key increase exponentially, so a 2048-bit key has 22048 possible combinations and will take correspondingly longer time to crack. However, with the recent advances in Quantum computing the dream of breaking encryption in a timely manner is close to becoming reality in the near future.

Introduction to Quantum Computing

So, what is this Quantum computing and what makes it so special? Quantum computing is an emerging technology field that leverages quantum phenomena to perform computations. It has a great advantage over conventional computing due to the way it stores data and performs computations. In a traditional system information is stored in the form of bits, each of which can be either 0 or 1 at any given time. This makes a ‘bit’ the fundamental using of information in traditional computing. A Quantum computer on the other hand uses a ‘qubit’ as its fundamental unit and unlike the normal bit, a qubit can exist simultaneously as 0 and 1 — a phenomenon called superposition (Freiberger, 2017). This allows a quantum computer to act on all possible states of a qubit simultaneously, enabling it to perform massive operations in parallel using only a single processing unit. In fact, a theoretical projection has postulated that a Quantum Computer could break a 2048-bit RSA encryption in approximately 8 hours (Garisto, 2020).

In 1994 Peter W. Shor of AT&T deduced how to take advantage of entanglement and superposition to find the prime factors of an integer (Shor, 1994). He found that a quantum computer could, in principle, accomplish this task much faster than the best classical calculator ever could. He then proceeded to write an algorithm called Shor’s algorithm that could be used to crack the RSA encryption which prompted computer scientists to begin learning about quantum computing.

Introduction to Current Cryptography

Current security of cryptography relies on certain “hard” problems—calculations which are practically impossible to solve without the correct cryptographic key. Just as it is easy to break a glass jar but difficult to stick it back together there are certain calculations that are easy to perform but difficult to reverse. For example, we can easily multiply two numbers to get the result, however it is very hard to start with the result and work out which two numbers were multiplied to produce it. This becomes even more hard as the numbers get larger and this forms the basis of algorithms like the RSA (Rivest et al., 1978) that would take the best computers available billions of years to solve and all current IT security aspects are built on top of this basic foundation.

There are multiple ways of classifying cryptographic algorithms but in this paper, they will be classified based on the keys required for encryption and decryption. The main types of cryptographic algorithms are symmetric cryptography and asymmetric cryptography.

Symmetric Cryptography

Symmetric cryptography is a type of encryption that uses the same key for both encryption and decryption. This requires the sender and receiver to exchange the encryption key securely before encrypted data can be exchanged. This type of encryption is one of the oldest in the world and was used by Julius Caesar to protect his communications in Roman times (Singh, 2000). Caesar’s cipher, as it is known is a basic substitution cypher where a number is used to offset each alphabet in the message. For example, if the secret key is ‘4’ then each alphabet would be replaced with the 4th letter down from it, i.e. A would be replaced with E, B with F and so on. Once the sender and receiver agree on the encryption key to be used, they can start communicating. The receiver would take each character of the message and then go back 4 letters to arrive at the plain-text message. This is a very simple example, but modern cryptography is built on top of this principle.

Another example is from world war II during which the Germans were encrypting their transmissions using the Enigma device to prevent the Allies from decrypting their messages as they had in the first World War (Rijmenants, 2004). Each day both the receiver and sender would configure the gears and specific settings to a new value as defined by secret keys distributed in advance. This allowed them to transmit information in an encrypted format that was almost impossible for the allied forces to decrypt. Examples of symmetric encryption algorithms include Advanced Encryption Standard (AES), Data Encryption Standard (DES), and International Data Encryption Algorithm (IDEA).

Symmetric encryption algorithms are more efficient than asymmetric algorithms and are typically used for bulk encryption of data.

Asymmetric Cryptography

Unlike symmetric cryptography asymmetric cryptography uses two keys, one for encryption and a second key for decryption (Rouse et al., 2020). Asymmetric cryptography was created to address the problems of key distribution in symmetric encryption and is also known as public key cryptography. Modern public key cryptography was first described in 1976 by Stanford University professor Martin Hellman and graduate student Whitfield Diffie. (Diffie & Hellman, 1976)

Asymmetric encryption works with public and private keys where the public key is used to encrypt the data and the private key is used to decrypt the data (Rouse et al., 2020). Before sharing data, a user would generate a public-private keypair and they would then publish their public key on their website or in key management portals. Now, whoever wants to send private data to them would use their public key to encrypt the data before sending it. Once they receive the cipher-text they would use their private key to decrypt the data. If we want to add another layer of authentication to the communication, the sender would encrypt the data with their private key first and then do a second layer of encryption using the recipient’s public key. The recipient would first decrypt the message using their private key, then decrypt the result using the senders public key. This validates that the message was sent by the sender without being tampered. Public key cryptography algorithms in use today include RSA, Diffie-Hellman and Digital Signature Algorithm (DSA).

Quantum Computing vs Classical Computing

Current state of Quantum Computing

Since the early days of quantum computing we have been told that a functional quantum computer is just around the corner and the existing encryption systems will be broken soon. There has been significant investment in the field of Quantum computers in the past few years, with organizations like Google, IBM, Amazon, Intel and Microsoft dedicating a significant amount of their R&D budget to create a quantum computer. In addition, the European Union has launched a Quantum Technologies Flagship program to fund research on quantum technologies (Quantum Flagship Coordination and Support Action, 2018).

As of September 2020, the largest quantum computer is comprised of 65 qubits and IBM has published a roadmap promising a 1000 qbit quantum computer by 2023 (Cho, 2020). While this is an impressive milestone, we are still far away from a fully functional general use quantum computer. To give an idea of how far we still have to go Shor’s algorithm requires 72k3 quantum gates to be able to factor a k bits long number (Shor, 1994). This means in order to factor a 2048-bit number we would need a 72 * 20483 = 618,475,290,624 qubit computer which is still a long way off in the future.

Challenges in Quantum Computing

There are multiple challenges in creating a quantum computer with a large number of qubits as listed below (Clarke, 2019):

  • Qubit quality or loss of coherence: The qubits being generated currently are useful only on a small scale, after a particular no of operations they start producing invalid results.
  • Error Correction at scale: Since the qubits generate errors at scale, we need algorithms that will compensate for the errors generated. This research is still in the nascent stage and requires significant effort before it will be ready for production use.
  • Qubit Control: We currently do not have the technical capability to control multiple qubits in a nanosecond time scale.
  • Temperature: The current hardware for quantum computers needs to be kept at extremely cold temperatures making commercial deployments difficult.
  • External interference: Quantum computes are extremely sensitive to interference. Research at MIT has found that ionizing radiation from environmental radioactive materials and cosmic rays can and does interfere with the integrity of quantum computers.

Cryptographic algorithms vulnerable to Quantum Computing

Symmetric encryption schemes impacted

According to NIST, most of the current symmetric cryptographic algorithms will be relatively safe against attacks by quantum computer provided a large key is used (Chen et al., 2016). However, this might change as more research is done and quantum computers come closer to reality.

Asymmetric encryption schemes impacted

Unlike symmetric encryption schemes most of the current public key encryption algorithms are highly vulnerable to quantum computers because they are based on the previously mentioned factorization problem and calculation of discrete logarithms and both of these problems can be solved by implementing Shor’s algorithm on a quantum computer with enough qubits. We do not currently have the capability to create a computer with the required number of qubits due to challenges such as loss of qubit coherence due to ionizing radiation (Vepsäläinen et al., 2020), but they are a solvable problem looking at the ongoing advances in the field and the significant effort being put in the field by companies such as IBM and others (Gambetta et al., 2020).

Post Quantum Cryptography

The goal of post-quantum cryptography is to develop cryptographic algorithms that are secure against quantum computers and can be easily integrated into existing protocols and networks.

Quantum proof algorithms

Due to the risk posed by quantum computers, the National Institute of Standards and Technology (NIST) has been examining new approaches to encryption and out of the initial 69 submissions received three years ago, the group has narrowed the field down to 15 finalists and has now begun the third round of public review of the algorithms (Moody et al., 2020) to help decide the core of the first post-quantum cryptography standard. They are expecting to end the round with one or two algorithms for encryption and key establishment, and one or two others for digital signatures (Moody et al., 2020).

Quantum Key Distribution

Quantum Key Distribution (QKD) uses the characteristics of quantum computing to implement a secure communication channel allowing users to exchange a random secret key that can then be used for symmetrical encryption (IDQ, 2020). QKD solves the problem of secure key exchange for symmetrical encryption algorithms and it has the capability to detect the presence of any third party attempting to eavesdrop on the key exchange. If there is an attempt by a third-party to eavesdrop on the exchange, they will create anomalies in the quantum superpositions and quantum entanglement which will alert the parties to the presence of an eavesdropper, at which point the key generation will be aborted (IDQ, 2020). The QKD is used to only produce and distribute an encryption key securely, not to transmit any data. Once the key is exchanged it can be used with any symmetric encryption algorithm to transmit data securely.

Conclusion

Development of a quantum computer may be 100 years off or may be invented in the next decade, but we can be sure that once they are invented, they will change the face of computing forever including the field of cryptography. However, we should not panic as this is not the end of the world as the work on quantum resistant algorithms is going much faster than the work on creating a quantum computer. The world’s top cryptographic experts have been working on Quantum safe encryption for the past three years and we are nearing the completion of the world’s first post-quantum cryptography standard (Moody et al., 2020). Even if the worst happens and it is not possible to create a quantum safe algorithm immediately, we still have the ability to encrypt and decrypt data using one-time pads until a safer alternative or a new technology is developed.

References

Chen, L., Jordan, S., Liu, Y.-K., Moody, D., Peralta, R., Perlner, R., & Smith-Tone, D. (2016). Report on Post-Quantum Cryptography. https://doi.org/10.6028/nist.ir.8105

Cho, A. (2020, September 15). IBM promises 1000-qubit quantum computer-a milestone-by 2023. Science. https://www.sciencemag.org/news/2020/09/ibm-promises-1000-qubit-quantum-computer-milestone-2023.

Clarke, J. (2019, March). An Optimist’s View of the Challenges to Quantum Computing. IEEE Spectrum: Technology, Engineering, and Science News. https://spectrum.ieee.org/tech-talk/computing/hardware/an-optimists-view-of-the-4-challenges-to-quantum-computing.

Diffie, W., & Hellman, M. (1976). New directions in cryptography. IEEE Transactions on Information Theory, 22(6), 644–654. https://doi.org/10.1109/tit.1976.1055638

Freiberger, M. (2017, October 1). How does quantum computing work? https://plus.maths.org/content/how-does-quantum-commuting-work.

Gambetta, J., Nazario, Z., & Chow, J. (2020, October 21). Charting the Course for the Future of Quantum Computing. IBM Research Blog. https://www.ibm.com/blogs/research/2020/08/quantum-research-centers/.

Garisto, D. (2020, May 4). Quantum computers won’t break encryption just yet. https://www.protocol.com/manuals/quantum-computing/quantum-computers-wont-break-encryption-yet.

IDQ. (2020, May 6). Quantum Key Distribution: QKD: Quantum Cryptography. ID Quantique. https://www.idquantique.com/quantum-safe-security/overview/quantum-key-distribution/.
Moody, D., Alagic, G., Apon, D. C., Cooper, D. A., Dang, Q. H., Kelsey, J. M., Yi-Kai, L., Miller, C., Peralta, R., Perlner R., Robinson A., Smith-Tone, D., & Alperin-Sheriff, J. (2020). Status report on the second round of the NIST post-quantum cryptography standardization process. https://doi.org/10.6028/nist.ir.8309

Nohe, P. (2019, May 2). What is 256-bit encryption? How long would it take to crack? https://www.thesslstore.com/blog/what-is-256-bit-encryption/.
Quantum Flagship Coordination and Support Action (2018, October). Quantum Technologies Flagship. https://ec.europa.eu/digital-single-market/en/quantum-technologies-flagship

Rijmenants, D. (2004). The German Enigma Cipher Machine. Enigma Machine. http://users.telenet.be/d.rijmenants/en/enigma.htm.

Rivest, R. L., Shamir, A., & Adleman, L. (1978). A method for obtaining digital signatures and public-key cryptosystems. Communications of the ACM, 21(2), 120–126. https://doi.org/10.1145/359340.359342

Rouse, M., Brush, K., Rosencrance, L., & Cobb, M. (2020, March 20). What is Asymmetric Cryptography and How Does it Work? SearchSecurity. https://searchsecurity.techtarget.com/definition/asymmetric-cryptography.

Shor, P. w. (1994). Algorithms for quantum computation: discrete logarithms and factoring. Proceedings 35th Annual Symposium on Foundations of Computer Science, 124–134. https://doi.org/10.1109/sfcs.1994.365700

Singh, S. (2000). The code book: The science of secrecy from Egypt to Quantum Cryptography. Anchor Books.

Vepsäläinen, A. P., Karamlou, A. H., Orrell, J. L., Dogra, A. S., Loer, B., Vasconcelos, F., David, K. K., Melville A. J., Niedzielski B. M., Yoder J. L., Gustavsson, S., Formaggio J. A., VanDevender B. A., & Oliver, W. D. (2020). Impact of ionizing radiation on superconducting qubit coherence. Nature, 584(7822), 551–556. https://doi.org/10.1038/s41586-020-2619-8


Note: This was originally written as a paper for one of my classes at EC-Council University in Q4 2020, which is why the tone is a lot more formal than my regular posts.

– Suramya
April 21, 2022

It is possible to plant Undetectable Backdoors in Machine Learning Models

Machine learning (ML) is the big thing and ML algorithms are slowly creeping into all aspects of our life such as unlocking your phone using facial recognition, evaluating the eligibility for a loan, surveillance, what ads you see when surfing the web, what search results you get when searching for stuff etc etc. The problem is that ML algorithms are not infallible they depend on the training data used, confirmational bias etc. At the very least they enforce the existing bias for example, if a company only hires men 25-45 for a role then the ML data set will take this as the input and all future candidates will be evaluated against this criteria because the system thinks that this is what a success looks like. The algorithms themselves are getting more and more complicated and it is almost impossible to review and validate the findings. Due to this decisions are being made by machines that can’t be audited easily. Plus it doesn’t help that most ML models are proprietary and the companies refuse to let outsiders examine them due to Trade secrets and proprietary information used in them.

Another problem is that these ML models is adversarial perturbations where attackers make minor changes to the image/data going in to get a specific response/output. There are a lot of examples of this in the past few years and some of them are listed below (Thanks to Cory Doctorow for consolidating them in one place)

These all take advantage of flaws in the ML model that can be exploited using minor changes in the input data. However, there is another major exploit surface available which is incredibly hard to protect against: Backdoors in the ML models by creating a model that will accept a particular entry/key to produce a specific output. The ‘best’ part is that it is almost impossible to detect if this has been done because the model will function exactly the same as an un-tampered model and will only show the abnormal behavior for the specific key which would have been randomly generated by the creator during the training. If done well then the modifications will be undetectable for most tests.

A team for MIT and IAS has written a paper on it (“Planting Undetectable Backdoors in Machine Learning Models“) where they go into details of how this can be done and the potential impact. Unfortunately, they have not been able to come up with a feasible defense against this attack as of this time. Hopefully that will change as others start focusing on this problem and how to solve it.

Given the computational cost and technical expertise required to train machine learning models, users may delegate the task of learning to a service provider. We show how a malicious learner can plant an undetectable backdoor into a classifier. On the surface, such a backdoored classifier behaves normally, but in reality, the learner maintains a mechanism for changing the classification of any input, with only a slight perturbation. Importantly, without the appropriate “backdoor key”, the mechanism is hidden and cannot be detected by any computationally-bounded observer. We demonstrate two frameworks for planting undetectable backdoors, with incomparable guarantees.

First, we show how to plant a backdoor in any model, using digital signature schemes. The construction guarantees that given black-box access to the original model and the backdoored version, it is computationally infeasible to find even a single input where they differ. This property implies that the backdoored model has generalization error comparable with the original model. Second, we demonstrate how to insert undetectable backdoors in models trained using the Random Fourier Features (RFF) learning paradigm or in Random ReLU networks. In this construction, undetectability holds against powerful white-box distinguishers: given a complete description of the network and the training data, no efficient distinguisher can guess whether the model is “clean” or contains a backdoor.

Our construction of undetectable backdoors also sheds light on the related issue of robustness to adversarial examples. In particular, our construction can produce a classifier that is indistinguishable from an “adversarially robust” classifier, but where every input has an adversarial example! In summary, the existence of undetectable backdoors represent a significant theoretical roadblock to certifying adversarial robustness.

The paper is still waiting for the peer-review to complete but the concept and methods they describe seem solid so this is a problem we will have to solve sooner rather than later considering the speed with which ML models are impacting our life.

Source: Schneier on Security: Undetectable Backdoors in Machine-Learning Models

– Suramya

April 19, 2022

Please stop taking such photos unless you have a death wish.

Filed under: My Thoughts — Suramya @ 12:04 AM

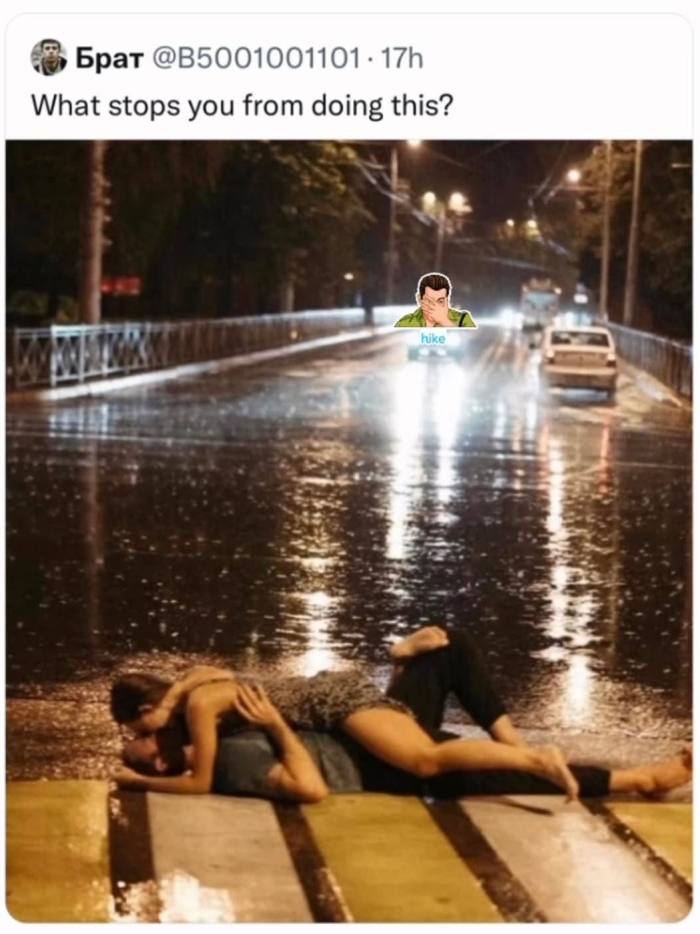
The following image popped up in my feed earlier today and I am dumbfounded by what people feel is ok to do to get a perfect (Instagram?) picture.


Answer: Common sense and a working brain

This looks like it is an active road, as you can see cars in the background and there are cars driving towards them. They are lying down on a zebra crossing, in the rain which will make it difficult for drivers to stop the car quickly. Plus since no one expects idiots to be lying down on the road there is a good chance that someone who is not paying attention or is momentarily distracted can run them over and in this pose it is almost impossible for these two to get out of the way fast if a car is about to run them down.

I have taken a few sitting on the road photos over the years, but we ensured that the roads were empty and we could see for a fair distance so that we could get out of the way if there was oncoming traffic.

Come on folks, is taking a great pic really worth dying for? Or do you want to be remembered as the idiots who got run over when taking an Instagram pic? Please stop this idiotic behavior.

– Suramya

April 18, 2022

Oracle releases a ‘free’ version of Oracle Solaris 11.4 for opensource developers and non-production personal use

Filed under: Linux/Unix Related,My Thoughts — Suramya @ 2:59 AM

Last month Oracle released a ‘free’ version of Oracle Solaris 11.4 for opensource developers and non-production personal use. The key point to note is that this doesn’t mean that there is a free/opensource version of the OS now available because unlike the Open Solaris project (that was released in 2008 but was discontinued) this build is a similar to a beta release and contains pre-release builds of a particular SRU (which I think means a release version). To me it sounds like they want the opensource community to perform free testing for their releases while getting some positive publicity.

I don’t think I will be trying it out because I don’t really trust Oracle. They are notorious for their bad takes and really aggressive enforcement of their IP rights. Plus their history with opensource projects has been bumpy and you never know when they will change their mind and go in a different direction.

My first experience with Unix/Linux was SunOS 4.1 followed by Solaris 5. I even had a Sparc machine at one point but it got lost during one of the many moves I made over the years. I loved the OS and since I couldn’t run it on my machines I started using Linux which was a great alternative. When OpenSolaris was released I received installation CDs to try it out, unfortunately life got in the way and I never really tested it out (other than the initial install). It was disappointing when the project went defunct & shutdown. I took a look at the OpenSolaris Wikipage and it looks like none of the derivative projects that were supposed to take over really went anywhere. So that sucks.

I don’t think that Unix does anything that Linux can’t do and even then if you want to run Unix on your machines I would recommend you go for FreeBSD instead of this ‘free’ version.

Thanks to HackaDay: Solaris Might Be Free If You Want It for the initial link.

– Suramya

« Newer PostsOlder Posts »

Powered by WordPress